


News
2026-11-12 17:23:00
The State Service for Special Communication and Information Security (XRİTDX) held training on the management of information security risks in Nakhchivan.
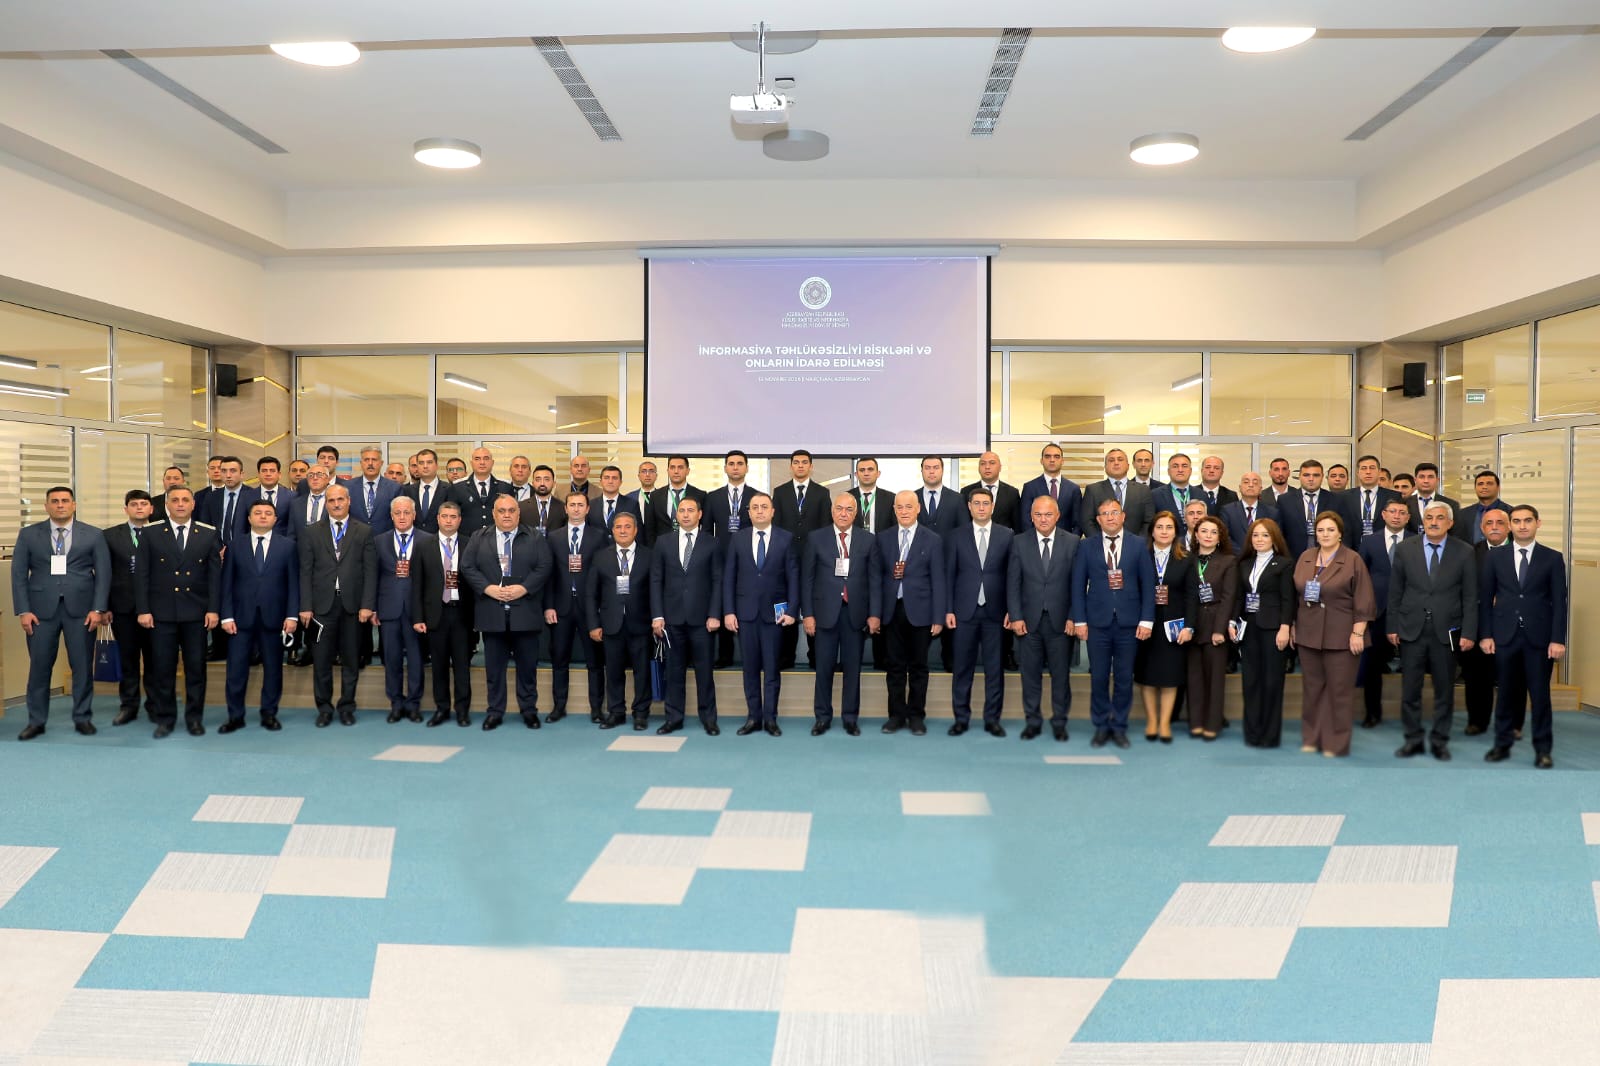
The State Service for Special Communication and Information Security (SSSCIS) of the Republic of Azerbaijan conducted a training session in the Nakhchivan Autonomous Republic for representatives of government agencies and higher education institutions, focusing on the management of information security risks.
The objective of the training was to enhance practical knowledge regarding the assessment of the current state of information security within government agencies in Nakhchivan, the identification and management of information security risks, and the development of a risk register, as well as to provide methodological support to these institutions.
Opening the event with an introductory speech, Lieutenant General Allahveran Ismayilov, Deputy Chief of the SSSCIS, briefed the participants on the requirements of the "Rules for Maintaining the Information Security Risk Register"—approved by Decision No. 411 of the Cabinet of Ministers of the Republic of Azerbaijan dated December 25, 2025—and outlined the tasks incumbent upon government agencies in this regard. A. Ismayilov stated that, in accordance with the Decision, state institutions are required—within a six-month period—to establish a registry of information security risks, identify existing threats and vulnerabilities, and define specific risk-mitigation measures, the individuals responsible for them, and the timelines for implementation.
During the training, the current situation and identified shortcomings were discussed, based on information provided by state institutions. Speaking at the event, Nadir Novruzov, a department head at the Special Communication and Information Security State Service (SCISSS), noted that information security is not ensured solely through the presence of technical tools or antivirus software. The primary priority is the protection of information assets, the accurate assessment of risks, and the implementation of systematic measures to address them.
Furthermore, information was provided regarding tasks related to updating the SCISSS’s "Threats and Solutions" catalog and evaluating the compliance of the risk registries developed by state institutions with regulatory requirements. XRİTDX continues its activities aimed at strengthening information security within government institutions, establishing a systematic approach to risk management, and ensuring compliance with regulatory requirements.


